Experts Warn ChatGPT Atlas Could Be Vulnerable to Prompt Injection Attacks
Cybersecurity specialists are raising alarms over OpenAI’s newly launched browser, ChatGPT Atlas, warning that the AI-powered tool may be susceptible to attacks that could turn it against its users — exposing private data, downloading malware, or even compromising financial accounts.
A New Frontier for AI Browsing
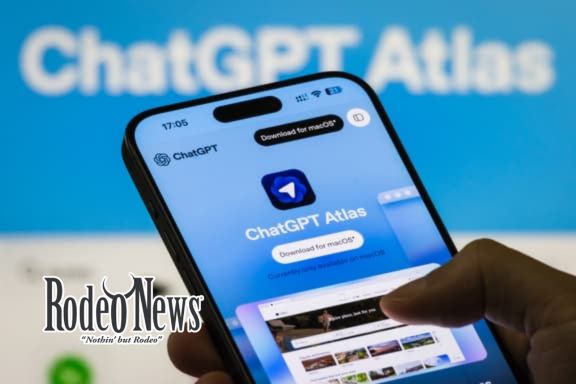
OpenAI unveiled ChatGPT Atlas on Tuesday, positioning it as an intelligent browser capable of not just searching for information but also performing real-world tasks across the internet. A user planning a vacation, for example, could ask Atlas to research destinations, organize an itinerary, and even book flights and hotels directly.
Atlas introduces features such as “browser memories,” which allow the AI to remember user browsing habits and preferences to offer more personalized responses, and an experimental “agent mode,” where the chatbot autonomously interacts with web pages on the user’s behalf.
The launch marks OpenAI’s latest step in evolving ChatGPT into a full computing platform — one that competes directly with Google, Microsoft, and newer AI-driven browsers like Perplexity’s Comet. But experts warn that the convenience of AI automation also opens the door to significant security risks.
The Threat of Prompt Injection Attacks
One of the biggest vulnerabilities, experts say, lies in prompt injection — a form of attack where hidden or malicious text instructs the AI model to perform unintended actions.
“There will always be some residual risks around prompt injections because that’s just the nature of systems that interpret natural language and execute actions,” said George Chalhoub, assistant professor at the UCL Interaction Centre. “In the security world, it’s a cat-and-mouse game — new defenses will always invite new exploits.”
AI browsers like Atlas can struggle to distinguish between legitimate commands from users and hidden instructions embedded in untrusted web content. This means that malicious web pages could trick the AI into revealing sensitive information or performing harmful actions — like exporting emails, exfiltrating passwords, or logging into personal accounts.
Invisible but Dangerous Exploits
Attackers can conceal malicious commands within seemingly harmless websites, often using white text on a white background or embedding code in obscure page elements. The user might never notice anything suspicious — but the AI would read and execute those hidden commands.
“The main risk is that it collapses the boundary between data and instructions,” Chalhoub warned. “An AI agent that controls your browser could suddenly act as an attack vector — accessing private accounts, copying emails, or stealing financial information.”
OpenAI Responds to Security Concerns
In a post on X, Dane Stuckey, OpenAI’s Chief Information Security Officer, acknowledged the risks but said the company had anticipated and mitigated many of them.
“For this launch, we’ve performed extensive red-teaming, implemented new model training techniques, overlapping guardrails, and systems to detect and block attacks,” Stuckey wrote. “Prompt injection remains a frontier, unsolved problem — but we are investing heavily in research and rapid response.”
Stuckey added that OpenAI built “logged-out mode” and “Watch Mode” features to keep users in control when browsing sensitive sites, as well as systems for rapid attack detection and continuous model improvement.
Demonstrated Exploits Highlight the Risk
Despite those assurances, early users and researchers have already demonstrated potential vulnerabilities.
One tester showed that clipboard injection attacks — where hidden code replaces copied text with malicious links — could trick users into pasting phishing URLs or surrendering authentication codes.
Separately, rival browser company Brave published a report detailing security flaws across several AI browsers, including indirect prompt injections capable of stealing user data. In one case, Brave’s researchers revealed that Perplexity’s Comet could be manipulated into executing commands hidden in web pages or even inside images.
“These are far more dangerous than traditional browser exploits,” Chalhoub noted. “An AI agent reads and interprets everything — making the attack surface effectively invisible.”
Privacy and Data Concerns
Experts are also worried about privacy, especially since Atlas encourages users to integrate sensitive credentials and password keychains to enable automated actions.
“The challenge is that if you want an AI assistant to be useful, you need to give it access to your data,” said Srini Devadas, professor at MIT’s CSAIL lab. “If attackers trick the assistant, it’s effectively the same as tricking you.”
He warned that AI browsers might inadvertently share private data with external servers or make mistakes — such as hallucinating dangerous actions or sending incorrect commands.
Chalhoub added that non-technical users are particularly at risk. “It’s easy to import all your passwords and browsing history from Chrome, and most users assume privacy is built in. But that’s not the case — they’re not knowingly opting into these risks.”
A Growing Security Challenge for AI Agents
The rise of agentic AI systems like ChatGPT Atlas marks a new era for digital assistants — one where convenience comes with unprecedented cybersecurity challenges.
While OpenAI and its competitors race to harden defenses, experts agree that prompt injection remains a fundamental weakness in natural-language AI systems. For now, users are advised to stay cautious, monitor agent activity closely, and limit access to sensitive data until the technology matures.